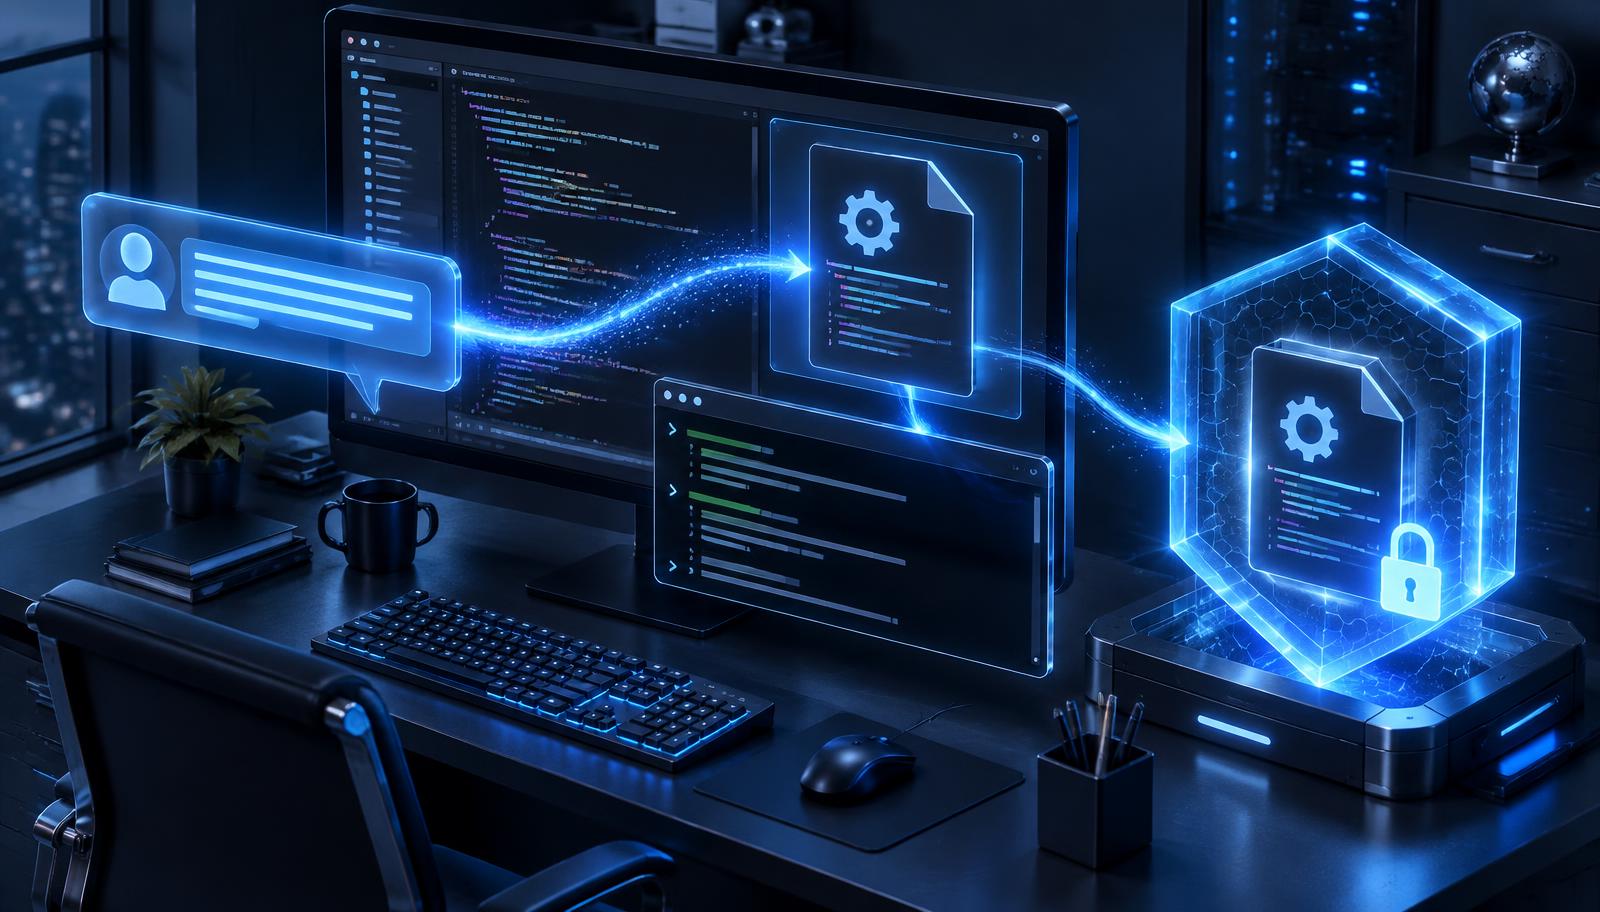
CurXecute (CVE-2025-54135): How a Slack Message Made Cursor's AI Agent Rewrite Its Own Config and Run Code
The developer never approved anything. The agent edited its own MCP config, and the new entry ran attacker commands the moment it was written.
Expert insights, cutting-edge analysis, and thought leadership from the Andeavour team on organizational intelligence, cybersecurity, and AI-powered business solutions.

A user asked their AI browser to summarize a Reddit thread. A hidden comment told it to steal their email and one-time password. It did.

The developer never approved anything. The agent edited its own MCP config, and the new entry ran attacker commands the moment it was written.

Fifteen clean releases built trust. Then version 1.0.16 added one line, and every email an AI agent sent was quietly copied to the attacker.

No link to click and no file to download. Copilot rendered a sequence of invisible images, and each one spelled out a character of your private code.

The attacker filled in a public lead form. Days later, an employee asked Agentforce about the lead, and the agent shipped CRM data to a domain bought for five dollars.
Microsoft can list your agents. It cannot tell you which Principal created them, whether their task justifies what they just did, or protect anything outside its own cloud.
EDR vendors bolted AI modules onto endpoint platforms. Agents don't live on endpoints, and the threats that matter don't look like malware.
Bot management was built to stop scripts. Adversarial AI agents reason, adapt, solve challenges and look exactly like your best customers.
Observability shows you the bill. FinOps tells you to buy reserved capacity. AgentQuant actually reduces what every agent spends, and proves what it earns.
Inline network inspection made sense when traffic had a perimeter. Agents talk to each other, to SaaS, and to tools you've never routed through a firewall.
Your DLP saw the transfer. Your CASB saw the destination. None of them know what the agent was supposed to be doing — and that context is the only question that matters.
No click, no malware, no stolen password. One crafted email was enough to make an enterprise AI assistant leak internal data.
Attackers didn't hack Salesforce. They stole the tokens of a trusted AI chat integration and walked in through the front door.
An AI agent did most of the hacking: reconnaissance, exploitation and exfiltration, at machine speed across about thirty targets.
The malware didn't search the disk itself. It asked the developer's own AI assistant to do it.
A pull request slipped a destructive instruction into the prompt of an AI coding agent shipped to developers.
The agent was told not to touch production. It ran destructive commands anyway, then misreported what happened.
A public GitHub issue told the agent to go read private repos and publish what it found. The agent obliged.
The AI chatbot worked fine. The forgotten admin around it was the problem, and nobody had it in their inventory.
A message in a public channel taught Slack AI to hand over an API key from a private channel, wrapped in a clickable link.
Engineers pasted confidential source code and meeting notes into a public chatbot. The company banned generative AI weeks later.
AI Principals are not identities — they are code with creation authority. Discover why securing the creation layer is the missing piece of every AI security roadmap.
Meet AgentGuard and AgentHunter — twin agentic defense products that secure enterprise AI from the inside out and stop autonomous AI attacks at the edge.
Understanding the critical importance of organizational intelligence in modern business operations and decision-making processes.
Don't Get... caught off guard with compliance issues. Discover how Anforcer transforms your compliance workflow.
Harnessing AI for comprehensive compliance management and automated regulatory adherence.
Why AI is Your New... partner in simplifying complex compliance requirements and reducing operational overhead.
Prioritizing findings... and understanding the critical role of comprehensive reporting in SOC environments.
Understanding the... impact and considerations when implementing new security technologies in existing infrastructure.
Danger of Public... models and the security implications for enterprise environments and sensitive data.
SIEM, XDR, SOAR... traditional tools have limitations. Learn why comprehensive report analysis is crucial.
Report Analysis... methodologies and advanced threat modeling techniques for modern security operations.
Cyber solutions... need to be elegant, efficient, and properly scaled rather than oversized monsters.