CamoLeak: How Hidden PR Comments Made GitHub Copilot Chat Smuggle Private Code Out, Pixel by Pixel
Key takeaways
- →Legit Security researcher Omer Mayraz showed that hidden comments in a pull request could take over GitHub Copilot Chat for any user who asked it about that PR.
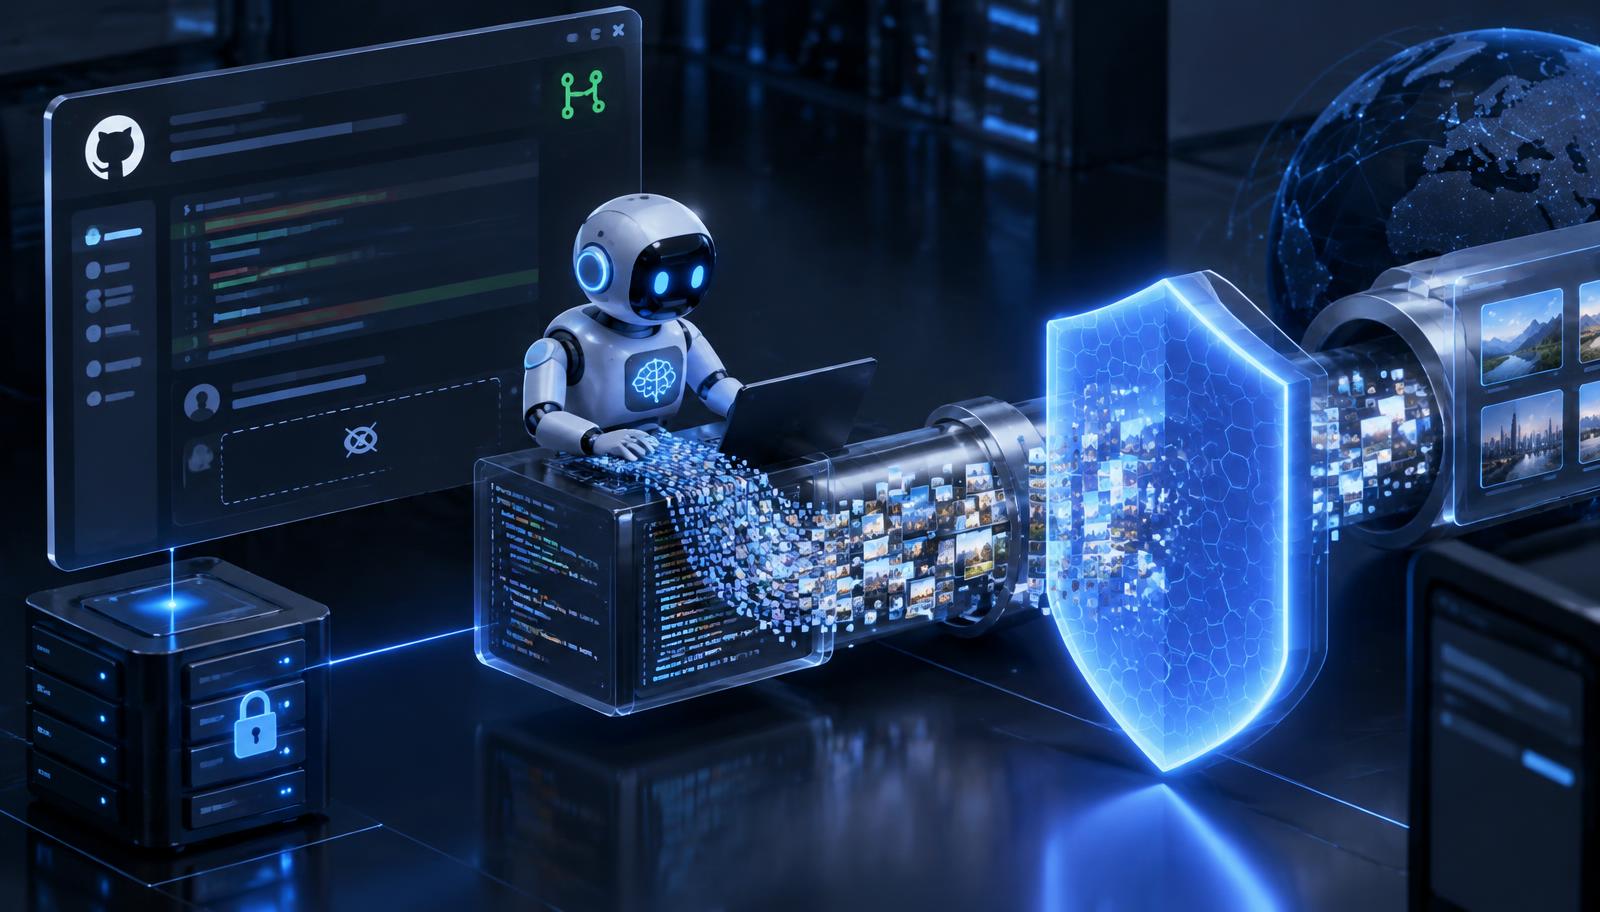
- →Copilot was made to search the victim's private repos for secrets, then encode them as a sequence of pre-signed Camo image URLs. Rendering the images leaked the data.
- →AgentGuard flags an AI assistant that reaches into unrelated private repositories and then emits high-volume, patterned outbound content that doesn't fit the user's question.
- 1
Attacker hides prompt in an invisible PR comment
- 2
Victim asks Copilot Chat about the pull request
- 3
Copilot searches victim's private repos for secrets
AgentGuard blocks out-of-task private-repo access and the patterned outbound image stream
- 4
Data encoded as ordered Camo image URLs
- 5
Images render; attacker server logs each character
- Affected
- GitHub Copilot Chat users (fixed by GitHub)
- When
- Fixed August 14, 2025 · disclosed October 8, 2025
- Impact
- Exfiltration of secrets, keys and private source code from repos the victim could access
What happened
GitHub lets pull-request descriptions contain hidden comments that don't show in the rendered view. Copilot Chat still reads them. Legit Security found that an attacker could plant instructions there, and any developer who later asked Copilot about the PR would run them with their own permissions.
GitHub's content security policy normally blocks images from arbitrary domains by routing them through its Camo proxy with signed URLs. Mayraz got around this by building a dictionary ahead of time: one valid signed Camo URL for every letter and symbol, each pointing at an attacker-controlled 1x1 pixel. The injected prompt told Copilot to find secrets such as AWS keys, or the description of an undisclosed zero-day, in the victim's private repositories, and to write them out as a sequence of those images. As the victim's browser loaded the pixels, the attacker's server read the secret one character at a time.
GitHub fixed the issue on August 14, 2025 by disabling image rendering in Copilot Chat. Legit published its findings on October 8, 2025, with a CVSS score of 9.6.
Why nothing caught it
Every request went to github.com infrastructure through GitHub's own proxy. No secret appeared in a single request, because it was spread across dozens of image loads. Secret scanners, DLP and network monitoring each saw something entirely ordinary.
- CSP passed: all images came from GitHub's own Camo
- No single request contained a recognizable secret
- The assistant used the victim's legitimate permissions
- The malicious prompt was invisible in the PR UI
How AgentGuard would have stopped it
AgentGuard's question is never just "is this request allowed?" It is "does this action fit what the agent was asked to do?" The user asked about one pull request. Copilot then searched other private repositories for credentials, which has nothing to do with that question, and the instruction came from untrusted PR content.
AgentGuard blocks that out-of-task retrieval at step three. If an agent did reach the output stage, AgentGuard also detects covert channels in agent output: long, ordered sequences of near-identical resource references that encode data. The pixels never load.
What to do Monday
Every AI assistant with repo access is an insider with perfect recall.
- Scope AI assistants to the repos the task requires
- Treat PR, issue and comment text as untrusted input
- Rotate any secrets that live in source code
- Monitor assistant output for encoded exfiltration
The lesson
Each of these attacks used an AI system that was doing exactly what it was allowed to do, on behalf of someone it should never have obeyed. Patches close one path at a time. AgentGuard closes the class: it judges every agent action against the agent's task, its Principal and its environment, with zero integration and deployment measured in days.
Frequently asked questions
What is CamoLeak?
CamoLeak is a CVSS 9.6 vulnerability in GitHub Copilot Chat found by Legit Security. Hidden PR comments could instruct Copilot to find secrets in a victim's private repos and leak them as a sequence of images routed through GitHub's Camo proxy. GitHub fixed it on August 14, 2025.
Why couldn't DLP or CSP stop CamoLeak?
All traffic went through GitHub's own trusted image proxy, and each request carried only one encoded character. No single request looked sensitive or came from a forbidden domain.
How does AgentGuard stop covert AI exfiltration?
AgentGuard blocks agent data access that falls outside the user's task. It also detects patterned output, such as ordered image-URL sequences, that encodes data for exfiltration.
See AgentGuard on your own environment
Zero integration. Live in days. We'll show you what your current stack is missing.