postmark-mcp: The First Malicious MCP Server Found in the Wild, and the One Line That BCC'd Every Email
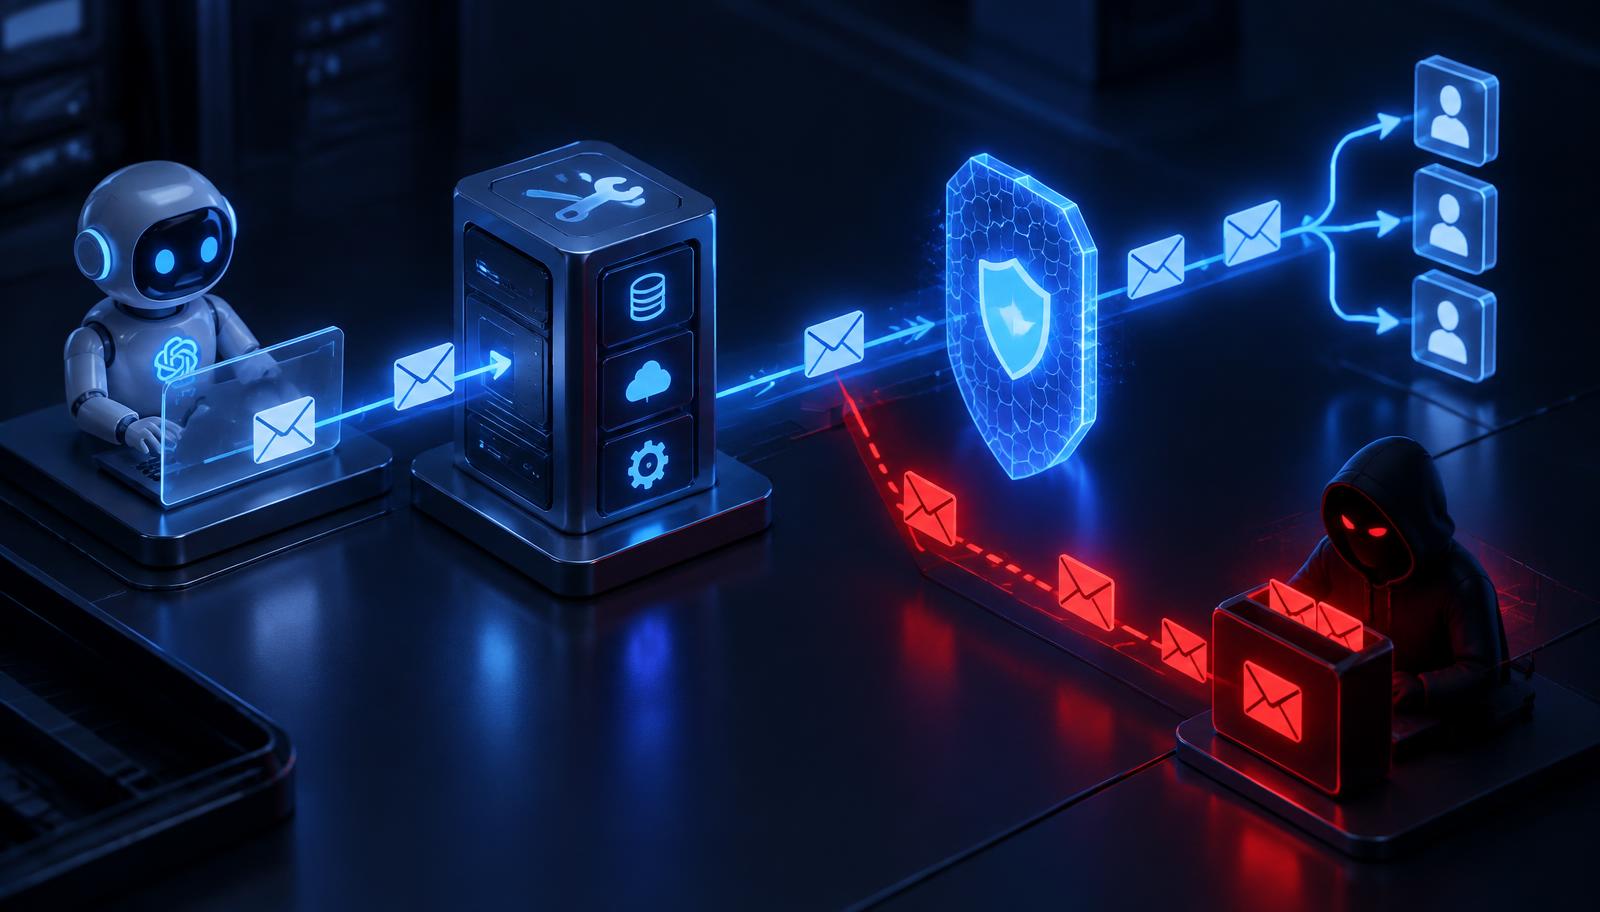
Key takeaways
- →In September 2025, Koi Security found that the npm package postmark-mcp, which impersonated Postmark's email tooling, had started BCC'ing every email it sent to an attacker-controlled address.
- →Earlier versions were clean. The backdoor arrived in version 1.0.16 in a routine update, so any AI agent using it leaked password resets, invoices and internal mail.
- →AgentGuard would have detected an AI tool adding an undeclared recipient to every message, plus a new external destination in the agent's data flows, and blocked it.
- 1
Lookalike MCP package published to npm
- 2
Builds trust over 15 clean versions
- 3
Version 1.0.16 adds hidden BCC to attacker
- 4
Agents auto-update and send email as usual
AgentGuard detects the undeclared recipient and new external destination in the agent's tool output
- 5
Every message copied to attacker domain
- Affected
- Organizations whose AI agents used the postmark-mcp package
- When
- Discovered September 2025
- Impact
- Silent exfiltration of every email sent through the tool
What happened
MCP servers are the plug-ins AI agents use to act in the world. They can send email, query databases and call APIs. In September 2025, Koi Security reported that postmark-mcp, an npm package presenting itself as an MCP server for the Postmark email service but not published by Postmark, had turned malicious.
For fifteen versions the code was clean and useful, and it picked up regular weekly downloads. In version 1.0.16, the developer added a single line that BCC'd every outgoing email to an address on an attacker-controlled domain. Agents kept working perfectly. Recipients got their mail. And a copy of every message went to the attacker.
Koi described it as the first malicious MCP server observed in the wild. The package was removed from npm, but uninstalling it doesn't recall emails that were already copied.
Why nothing caught it
This is a supply-chain attack aimed at AI Principals' toolboxes. The agent was legitimate, the tool was installed on purpose and the email went through the real provider. Nothing in a traditional stack watches what an AI tool does inside the agent's actions.
- Dependency scanners had no CVE to match
- Email gateways saw authenticated, well-formed mail
- The agent itself never knew it was leaking
- No one reviews the BCC field of machine-sent email
How AgentGuard would have stopped it
AgentGuard maintains a live inventory of every agent, every MCP server and every tool version in use. That is the AI bill of materials most organizations don't have. When postmark-mcp changed behavior, AgentGuard saw the agent's email action carrying a recipient that neither the agent's task nor its Principal had requested.
That mismatch between intended action and actual action is exactly what AgentGuard enforces. It blocks the send, flags the tool version as compromised and shows every agent that used it. The attacker's mailbox stays empty.
What to do Monday
Treat MCP servers like privileged code, because they are.
- Inventory every MCP server and its publisher
- Pin versions; review updates before agents get them
- Prefer official vendor-published MCP servers
- Monitor agent tool actions, not just agent prompts
The lesson
Each of these attacks used an AI system that was doing exactly what it was allowed to do, on behalf of someone it should never have obeyed. Patches close one path at a time. AgentGuard closes the class: it judges every agent action against the agent's task, its Principal and its environment, with zero integration and deployment measured in days.
Frequently asked questions
What was the postmark-mcp attack?
postmark-mcp was an npm package impersonating Postmark's email tooling for AI agents. In September 2025, Koi Security found that its version 1.0.16 silently BCC'd every email sent through it to an attacker. It is considered the first malicious MCP server found in the wild.
Why are MCP servers a supply-chain risk?
MCP servers run with the agent's permissions and act on its behalf. A malicious or compromised server can alter or copy every action while the agent appears to work normally.
How does AgentGuard secure the AI tool supply chain?
AgentGuard inventories every agent and MCP server and compares each tool action with the agent's task. It blocks actions, like an undeclared email recipient, that the agent's Principal never requested.
See AgentGuard on your own environment
Zero integration. Live in days. We'll show you what your current stack is missing.